Approval workflow software for the decisions you do not want made alone.
Quotes, invoices, payments, and discounts are explicit permissions in NoxOrigin, and actions that carry financial or operational risk can require a manager approval or a supervisor override — recorded, so the exception is reviewable afterwards instead of invisible. Built for small teams that have outgrown a shared login.
Why informal approval stops working
The owner cannot personally approve every transaction, so staff use their own judgement. That is not misconduct — it is the predictable result of a control that only exists in conversation. The fix is a threshold that is faster to use than the workaround.
The permission and the practice drift apart
The written rule says discounts need approval. The counter needs a decision now. So staff decide, and the written rule becomes a document nobody opens.
Approvals are granted but not recorded
An approval nobody can see later is indistinguishable from one that never happened, which makes the first dispute unwinnable.
Overrides happen silently
When the owner does approve something verbally, there is no trace of it. The exception exists, but the record has no idea.
Exceptions get averaged away
A pattern of approved discounts is buried inside a monthly total that still looks fine. The number is correct and the information is gone.
From permission to reviewed exception
Six steps, and every one of them is a decision you make rather than a setting we pick.
Write down the decision, not just the permission
Role, threshold, the reason an exception is allowed, and who approves it. An approval rule nobody can explain in a meeting will be bypassed in a week.
Set the threshold that matches your margin
Discount approval gates who may reduce a price. Routine adjustments stay with staff; the ones that change your week get routed.
Bring it to the person entitled to decide
NoxOrigin holds the permission that stops the wrong person acting and the audit entry that records who did. It does not route an exception to anybody on its own: someone asks, waits, or decides in the moment. The hand-off is human, and the record of it is not.
Record the override
When a supervisor overrides a blocked action, it is written to the audit trail with who and against what, so it can be reviewed later rather than defended from memory.
Review the exceptions, not the approvals
Most approvals are uneventful. What is worth reading is who approved what, and whether the pattern tells you the threshold is in the wrong place.
Retire the controls that no longer earn their place
Permissions and habits both accumulate faster than processes are retired. Schedule a review of who holds which permission rather than waiting for somebody to complain about it.
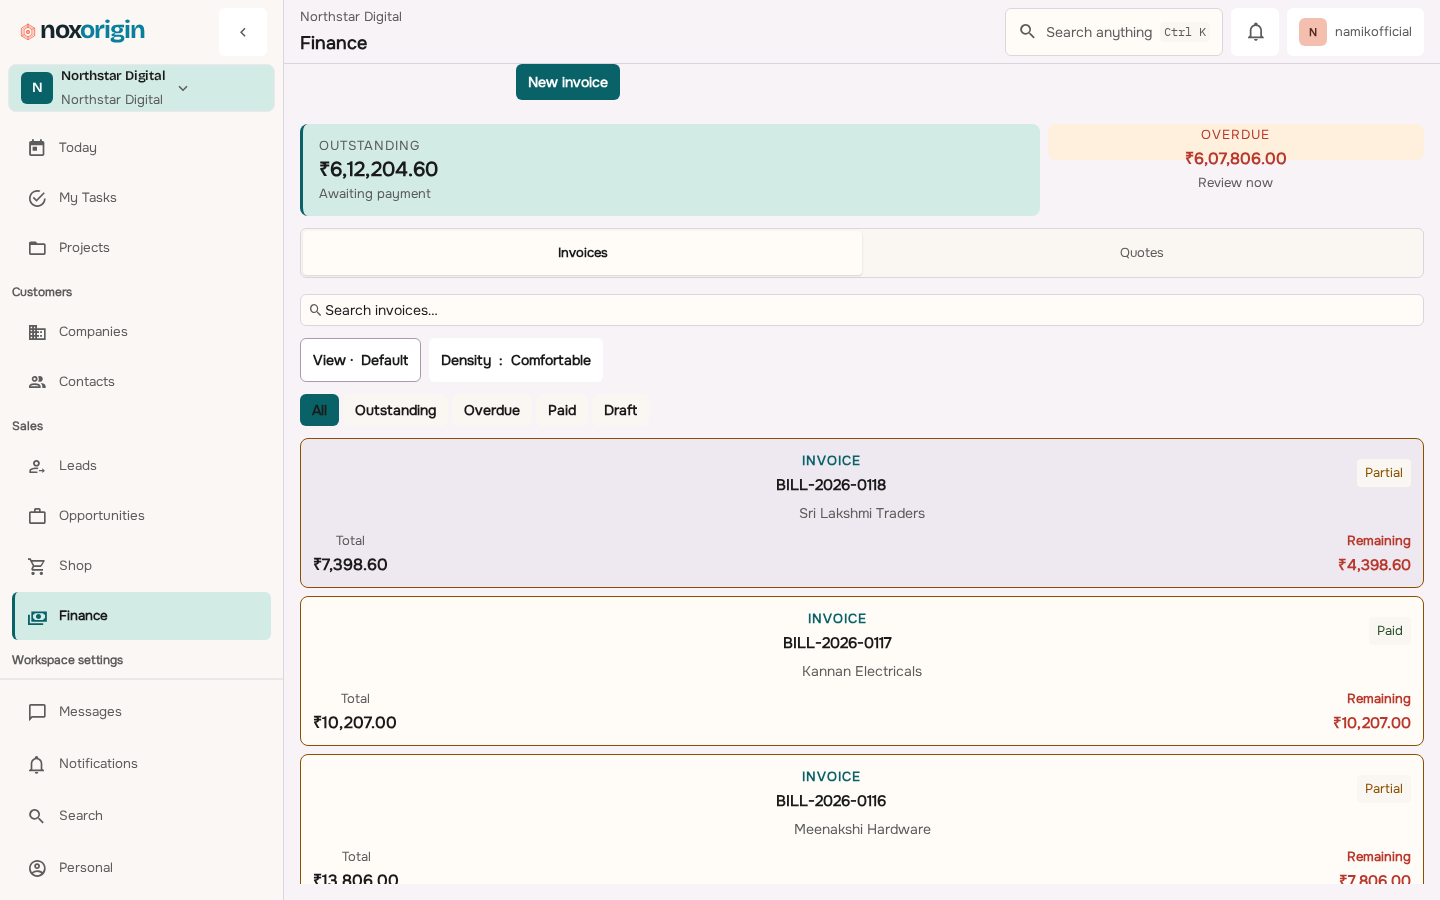
Approvals, exceptions, and audit in one review surface
Shown from a dedicated Nox-Billings deployment, which remains available as a scoped custom deployment for counter operations. In the unified NoxOrigin app, the same controls live in Platform; there is no Automations area.
Where this is the wrong tool
Some approval problems need a different kind of product, and finding that out early is cheaper than finding it out at rollout.
Not a process-mining, BPMN, or rule-engine suite
NoxOrigin has no rule engine to restrict: nothing is configured, nothing fires, and there is no model to draw. What it holds is permissions and audit — who may act, and who did. There is no graphical process map to model a whole organisation in, and nothing to configure into one.
Not an HR or expense product
Leave requests, expense claims, and payroll approvals are outside what this record chain covers. NoxOrigin is an operating system for work and money, not a people-management system.
Approvals do not fix bad policy
If the threshold is set so tightly that staff route around it, the control is theatre. Setting the right threshold is an operating decision, and we will help you reason about it rather than ship a default.
It does not replace a control framework
For regulated environments needing segregation-of-duties evidence across a full audit period, this is one layer of an operational record — not a compliance product, and we will not present it as one.
Read the permission split before you configure it
The published permission matrix is the fastest way to see how a cashier, manager, and owner are usually separated — and where the boundaries genuinely need deciding.
Approval workflow questions
What actually needs an approval in a small business?
Usually the actions that move money or commit the business: raising a quote below your floor, creating an invoice, recording a payment, applying a discount beyond a normal range, or a stock adjustment. NoxOrigin treats those as explicit permissions and lets a threshold route them to a person, so the counter keeps serving the customer while the judgement stays where it belongs.
Is this a general workflow or BPMN engine?
No, and it is worth being precise about why, because it is the same answer for a different reason than the one usually given. NoxOrigin has no rule engine of any kind: nothing is configured, nothing fires, and there is no vocabulary to restrict. What it has is permissions and audit — who may apply a discount or approve a quote, and who did. That is a smaller mechanism than a rule engine and a different one. If you need BPMN, form builders, or a general case-management workflow, this is not the product and we would rather say so early.
What happens when someone overrides a blocked action?
A supervisor can override a blocked action when the situation demands it, and the override is recorded. The important property is not that overrides exist — it is that a later reviewer can see that one happened, who made it, and against what. An unrecorded override is functionally identical to no control at all.
Will staff just find a workaround instead of asking?
That is a real risk and it is a policy problem before it is a software one. If the only way to reduce a price is a phone call to the owner, expect that path to keep being used. The approval has to be faster than the workaround, which usually means a low threshold that a manager can clear in seconds and a high threshold that genuinely needs the owner.
Can anything approve itself, unattended?
Nothing does, because there is nothing running to do it. NoxOrigin holds the permissions that stop an action the wrong person attempts and the audit record that shows who acted; it does not hold a threshold that approves anything by itself, and it does not hold a rule that could be given the power. A person decides every time, which is slower and is the actual product today.
Is this only for businesses with many employees?
No. It is aimed at businesses where one person currently holds everything and everyone else shares a login, which is common well before headcount justifies a full governance suite. The published permission matrix is designed to be read by a small team, not administered by one.
Name the three actions you least want decided alone.
Bring your current informal rules. We will map them to explicit permissions, set thresholds with you, and show what the audit history will let you review later.